On 25th February 2026 the United States Federal Trade Commission announced that it would not enforce the parental consent requirements of the Children’s Online Privacy Protection Rule against operators collecting personal information for the sole purpose of establishing how old a user is.
On 29th April 2026 the European Commission urged every Member State to place a privacy-preserving age verification application in citizens’ hands by the end of the year.
Both answer a question Kenyan law raised in 2019 and has never answered: how is a controller to discover that a user is a child without processing the very data the law protects because the user is a child?
The Development
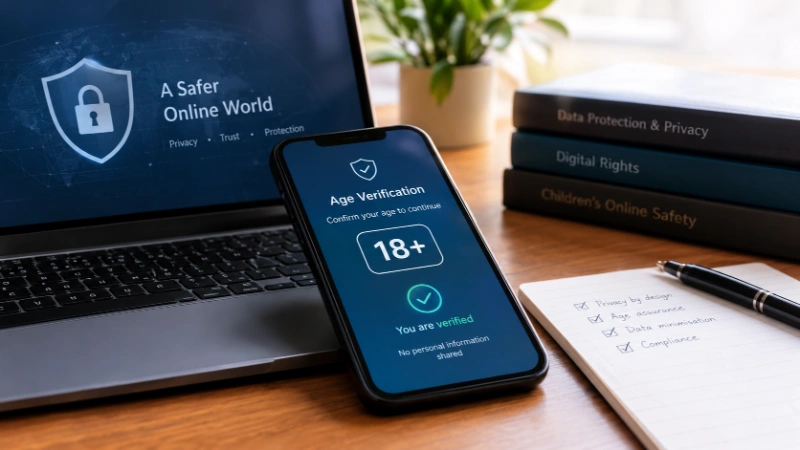
Europe’s answer is architectural. A blueprint published on 14th July 2025, alongside the Commission’s Guidelines on the protection of minors under the Digital Services Act, became feature-ready on 15th April 2026; built on the European Digital Identity Wallet specifications, it lets a user prove he or she is over eighteen without disclosing any other personal information.
America’s answer is administrative, conditioned on sole-purpose use, prompt deletion, vetted third parties, notice, security and accuracy. Enforcement follows, from preliminary findings against Meta in April 2026 to Australia’s under-sixteen restrictions, in force since 10th December 2025. The direction of travel is uniform: from asking a user’s age to assuring it.
These developments reflect a wider regulatory focus on children’s online safety and digital platform obligations, particularly as platforms face increasing pressure to protect minors without undermining their privacy rights.
The Circularity at the Heart of Section 33
Section 33(1) of the Data Protection Act prohibits processing a child’s personal data unless the parent or guardian consents and the processing advances the child’s best interests; section 33(2) requires “appropriate mechanisms for age verification and consent”; and section 33(3) leaves those mechanisms to available technology, data volume, the proportion likely to belong to children, the possibility of harm and such factors as may be specified by the Data Commissioner. These obligations are part of the broader duty of data controllers to protect children’s personal data and obtain appropriate parental or guardian consent, including when determining whether the processing is necessary and in the child’s best interests.
To know whether section 33(1) is engaged, a controller must process data capable of revealing that the user is a child, which, if the user is a child, is the very processing the section forbids without the consent the controller is trying to establish it needs. The only express relief, section 33(4), covers counselling and child protection services alone. That is the gap the Federal Trade Commission closed by forbearance; Kenya has no comparable instrument, the ODPC’s Guidance Notes for Processing Children’s Data (2025) being advisory and creating no safe harbour.
An Undeclared Threshold of Eighteen
The Act does not define “child”. Article 260 of the Constitution and the Children Act (Cap. 141) supply the definition, and it is eighteen. Kenya thus applies the most demanding parental consent threshold of the major regimes, against thirteen under the American Rule and thirteen to sixteen under Article 8 of the General Data Protection Regulation, on the thinnest machinery for giving effect to it; imported compliance programmes under-shoot by between two and five years of a user’s life. Article 53(2) cuts both ways, an indiscriminate gate excluding a seventeen-year-old from health and civic information as surely as it shields a nine-year-old from harm.
Four Regimes, One Application
A single Kenyan application can engage four age-assurance regimes at once. First, data protection: section 33, Regulation 13(2) of the Data Protection (General) Regulations, 2021 and Regulation 49(1)(e), which makes an impact assessment mandatory. Second, communications: the Communications Authority’s Industry Guidelines for Child Online Protection and Safety (2025), binding ICT licensees and content developers to age-verification protocols, parental controls and periodic returns. Third, gambling: the Gambling Control Act, No. 14 of 2025 and its draft 2026 operations regulations, which at Regulation 85 require identity, location and age to be confirmed against “reliable, independent and electronically verifiable data sources prior to player account activation”. Fourth, the criminal perimeter in the Children Act and the Computer Misuse and Cybercrimes Act (Cap. 79C), from which the Court of Appeal excised sections 22 and 23 on 6th March 2026. Two are non-binding, none interoperable, and the only one with technical content serves the narrowest sector.
Attestation or Identity Document, and the Australian Warning
There are two ways to build an age check: the relying party receives a document and holds it, or it receives an answer while a trusted source holds the document. Europe chose the second; Kenya’s only specific instrument chose the first, Regulation 85(4) requiring verification to “include official identification documents”.
Both verify, but only one survives the minimisation principle in section 25, and the first converts a child-protection duty into a national store of identity documents held by commercial operators. Section 33(3) reserves to the Data Commissioner the power to settle this once, for every sector; unexercised since 2019, it leaves the question to sector regulators holding no privacy mandate. Australia shows the cost of a weak assurance layer: three months after its under-sixteen ban took effect, use of age-restricted platforms had fallen only from about 86 to a little over 81 per cent, and about half of those who kept their accounts said their age was never checked.
PRACTICAL IMPLICATIONS
- Treat the ODPC Guidance Notes as the working standard. They alone identify acceptable methods and require each to be proportionate, privacy preserving and minimised. A choice documented against them is defensible; an undocumented one is not.
- Design the check to return an answer, not a document. Retain the result rather than the evidence, and delete the evidence the moment the check completes. Collecting identity documents where a yes-or-no response would suffice is difficult to defend against section 25 of the Act.
- Apply the Kenyan threshold of eighteen, treat parental consent under section 33(1) as a condition additional to the lawful basis under section 30 rather than a replacement for it, and run the Regulation 49(1)(e) impact assessment on the age check itself.
- Map the product against all four regimes and build to the strictest. There is no Kenyan safe harbour for age-verification data; the Federal Trade Commission’s statement is a United States enforcement policy with no application here.
Kenya did not wait for the world to legislate on children’s data. It legislated first, in 2019, and then stopped. What section 33 now needs is not a further prohibition but a standard, and the power to set that standard has been sitting unused in subsection (3) for seven years.
This article is provided free of charge for information purposes only; it does not constitute legal advice and should not be relied on as such. No responsibility for the accuracy and/or correctness of the information and commentary as set out in the article should be held without seeking specific legal advice on the subject matter. If you have any query regarding the same, please do not hesitate to contact our W&A Data Protection & ICT Law Department WAICTLaw@wamaeallen.com.
About the author
Janeirene specializes in real estate and securitization and banking and finance. She is a promising transactional advocate who has experience in real estate and securities law, transactional law and advisory and has handled complex transactions and advisories.
Peris is a results-driven and disciplined legal professional committed to delivering exceptional value to clients. With expertise across various legal fields, she provides strategic legal solutions tailored to diverse client needs. Her strong interpersonal skills, dedication, and meticulous approach to legal practice enable her to navigate complex legal matters effectively.
Denis Mutugi specializes in Commercial Litigation and Alternative Dispute Resolution.
Denis graduated with a Bachelor of Laws, LLB (Hons) from The University of Nairobi in 2021 and was admitted to the Roll of Advocates of the High Court of Kenya in the year 2023.
Denis has amassed a considerable wealth of experience in conducting legal research on various complex legal matters touching on Commercial, Insurance, Employment and Insolvency law and bankruptcy.